

Stop Auditing the Past. Continuously Monitor Reality.
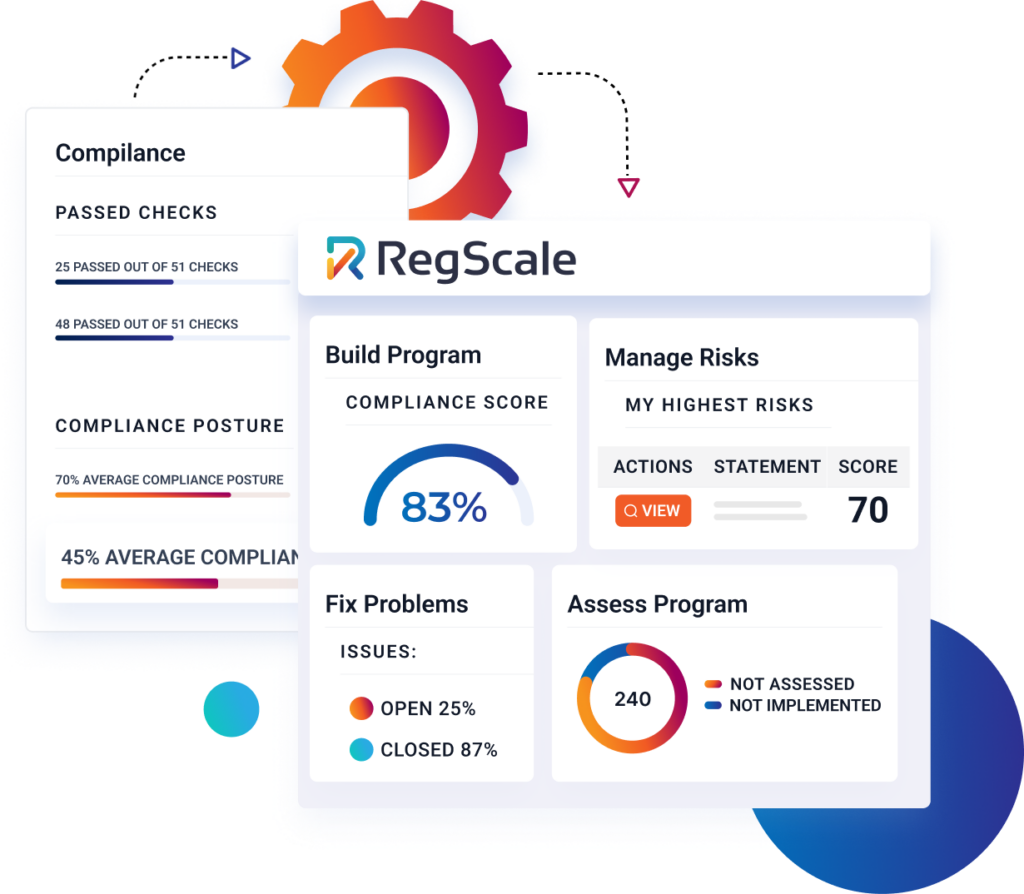
Cyber resilience isn’t a checklist. AI-driven attacks compromise systems in minutes, not months. RegScale’s Continuous Controls Monitoring platform connects live cloud telemetry, security tools, and CI/CD pipelines directly to federal and commercial compliance frameworks—giving you the speed to see, understand, and react in real time.
Trusted by the most secure and compliant organizations on the planet
The Velocity of Attack Has Changed. Your Compliance Architecture Must Change with It.
AI-speed attacks and real-time regulatory proof are converging. Annual audits are now a liability.
for AI-driven attacks to exploit a gap
for an annual audit to find it
Regulators now demand continuous proof.
Machine-readable, or out.
1,000-page Word documents cannot keep pace.
Continuous, or no contract.
Show continuous monitoring to win programs.
Personal liability.
Executives own unmonitored ICT supply chains.
Where Traditional GRC Breaks. How RegScale Fixes It.
Compliance Theater vs. Actual Cyber Risk
Passing an annual audit doesn’t stop an Advanced Persistent Threat (APT) or ransomware. Companies spend months compiling static artifacts to win a paper badge, while critical configuration drift and unpatched CVEs expose production systems between audits.
The RegScale Solution
RegScale connects to live security telemetry 24/7/365. Controls are validated continuously against technical reality, transforming compliance into a live defensive posture.
The Audit Fire Drill
Sixty days before an audit, engineering stops building to screenshot AWS, GitHub, and Okta settings.
The RegScale Solution
Automated API ingestion pulls evidence continuously, so engineering never pauses development before or during an audit. Teams keep shipping, avoid the lost sprints and delayed releases that audit prep causes, and the evidence locker is already complete when the auditor arrives.
Static Documentation Drift
Traditional System Security Plans (SSPs) are authored in Word docs or static PDFs. The moment an engineer pushes a new microservice or updates a Kubernetes cluster, the 500-page document is completely obsolete.
The RegScale Solution
RegScale stores security packages natively in NIST OSCAL code. When your infrastructure changes in GitOps, your System Security Plan dynamically updates itself in real time.
The DevSecOps Chasm
Engineers build via CI/CD, GitOps, and CLI tools. GRC officers work in spreadsheets and slow ticketing monoliths. Compliance slows down deployments, and engineers bypass GRC to ship on time.
The RegScale Solution
RegScale delivers Compliance as Code directly into the developer’s CI/CD pipeline via native CLI and GitHub Actions. Regulatory violations fail pull requests before code reaches production.
A Cohesive Enterprise Platform.
Never Outgrow Your GRC.
Point solutions work until your needs change: a new framework, a federal contract, your first serious audit. Then you migrate. RegScale is organized around your systems, not a single framework, so you add frameworks, authorizations, and business units without replatforming. One platform unites continuous monitoring, tool orchestration, and customer-facing trust.
RegScale CCM Platform
The core Continuous Controls Monitoring operating system. Houses the multi-framework crosswalk, RegML regulatory AI, dynamic risk ledger, and native NIST OSCAL dynamic SSP engine.
- Continuous monitoring across 250+ frameworks, supported out of the box
- RegML autonomous control cross-mapping & POA&M remediation
- Machine-enforced Open Policy Agent (OPA) Rego evaluation
- Continuous ATO (cATO) digital package generator
Orchestration Hub
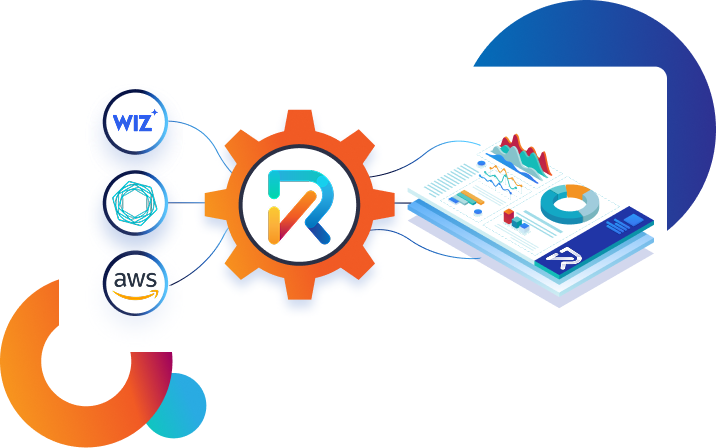
The automated integration backbone. Connects 100+ enterprise cloud environments, cybersecurity scanners, identity providers, and CI/CD pipelines via real-time pipeline event pushes and scheduled daily security tool pulls.
- Bi-directional API connectors into AWS, Azure, GCP, K8s
- Automated scheduled pulls from CrowdStrike, Tenable, Wiz, Qualys, and more
- Real-time GitOps & CI/CD pipeline push webhooks (GitHub, GitLab, Jira, ServiceNow)
- Cryptographic SHA-256 digital evidence hashing
RegScale Trust Center
Turn your real-time compliance posture into a commercial competitive advantage. RegScale Trust Center is a live, customer-facing security portal with automated NDA gating and self-service compliance artifacts, with best-in-class support for FedRAMP 20x and CR26 Rules.
- Real-time verified security posture badges for customers
- Automated click-through NDA workflow for audit reports
- Eliminates 90% of manual customer security questionnaires
- Powered by live telemetry data—never stale or out of date
Under the Hood: The 6 Software Engines
Every RegScale deployment contains six deterministic software engines.
Continuous Telemetry Ingest
Real-time pushes and daily syncs.
Automated OPA Evaluation
Deterministic policy checks on live state.
Universal Framework Crosswalk
One evidence set, 250+ frameworks.
Compliance as Code
OSCAL drives IaC. Pipelines block drift.
Dynamic Workflow and Threat-Based Risk Modeling
Signal approvals. Live, threat-based risk.
AI and Model Context Protocol (MCP) Engine
20+ agents. Secure LLM access.
Implement Once. Comply Everywhere.
Stop re-auditing the exact same security control across multiple compliance standards. RegScale’s universal crosswalk automatically maps your real-time telemetry across 250+ frameworks.

NIST SP 800-53
Rev 4 & Rev 5 Baselines with automated OSCAL profiles
FedRAMP Class D (High)
3-4x faster authorization with 20x modernization support
DoD CMMC 2.0
Level 2 readiness for defense contractors

SOC 2 Type II
Continuous Trust Services criteria monitoring with zero fire drills
EU DORA & NIS2
Continuous operational resilience and ICT supply-chain auditing
Trusted By Leaders Who Demand Defensible Security
Hear from CISOs, CTOs, and compliance architects who transformed their organizations from manual checklist drag into automated, continuous cyber resilience.
“When we began preparing for our CMMC audit, we knew the documentation burden would be significant. RegScale proved to be an invaluable partner in turning compliance from an ongoing administrative tax into an automated, defensible operating process.”
Charles Onstott
EVP & Chief Technology Officer, CALIBRE Systems
“Before RegScale, running SOC 2 and FedRAMP out of spreadsheets and Word docs meant a massive, manual documentation nightmare. RegScale’s continuous controls monitoring gives us real-time posture awareness without burning out our engineering team.”
Dennis Shewmaker
Former CTO / CISO, Tovuti LMS & Panjiea
“RegScale’s focus on continuous controls monitoring is critical for organizations navigating increasingly complex regulations. Achieving FedRAMP High readiness in months instead of years proves the power of Compliance as Code.”
Kevin Magee
Global Director, Cybersecurity Startups, Microsoft
The Benefits: What You Actually Get
When you replace manual checklist compliance with Continuous Controls Monitoring, your enterprise unlocks dramatic operational, defensive, and financial outcomes.
Permanently eliminate the 60-day panic before external audits. Evidence is continuously collected, hashed, and mapped in real time. When auditors arrive, your evidence locker is 100% pre-validated.
Compress federal and defense authorization timelines from an industry average of 14 months down to 3.5 months. Win government and defense contracts quarters ahead of competitors.
Catch security posture drift on every CI/CD deployment and daily security tool sync, instead of discovering vulnerabilities months later during an annual audit.
Banish manual Word questionnaires from the engineering workflow. Shift-left compliance as code into CI/CD runners so software teams ship rapidly without sacrificing regulatory compliance.
Reclaim 8,000+ senior engineering hours each year and slash external 3PAO auditor billing fees by $180,000. Typical enterprise deployments achieve full payback in under 3 months.
Deflect tedious vendor security questionnaires with a live, customer-facing Trust Center that provides cryptographic proof of real-time security posture.