

Machine-Readable Is Not the Same as Usable: Closing the VDR/VER Gap Before December 7

November 10, 2026

12:00pm ET
Your FedRAMP package has a second audience that never sits in your building: the authorizing official and RMF team who have to review it. Many agencies are still working out how to ingest machine-readable data, map it into their ATO process, and staff the review. Providers who make that job easy get adopted. Providers who don’t risk being asked for the old paperwork.
The timing is tight. VDR and VER become mandatory on December 7, 2026 under CISA BOD 26-04, with a corrective-action-plan grace period to March 7, 2027. CR26 becomes mandatory on January 1, 2027. New certifications comply from that date, and existing Rev 5 providers phase in through 2027. From the day of this session, that is 27 days to December 7.
In this session, three RegScale practitioners explain what VDR and VER require, how reviewers read your findings, and how to build a plan backward from your own dates.
What you’ll walk away with
- Why a machine-readable package is not automatically a usable one, and what a reviewer needs from yours
- How VDR and VER split the work: VDR is how you find and fix, VER is how you rate and report
- How every finding gets a Potential Agency Impact rating (N1 to N5), and how that rating and its remediation due date are derived
- How to seed the rating math so false criticals don’t crowd your queue, and how overrides are justified and audited
- The pitfalls that trip providers before December 7, and what to do today
- A reverse-timeline method you can take back to your team the same day
Register Now
Trusted by the most secure and compliant organizations on the planet
Speakers
-
Dale Hoak
CISO
RegScale

-
Kylie Hunter
Solutions Advisor
RegScale
-
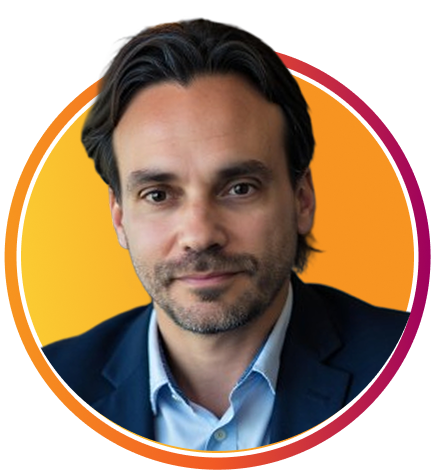
Chad Litoborski
Product Solutions Owner
RegScale
More ways to stay up to date
Get insights delivered to your inbox
Receive platform tips, release updates, news and more