CMMC Compliance, Built to Scale
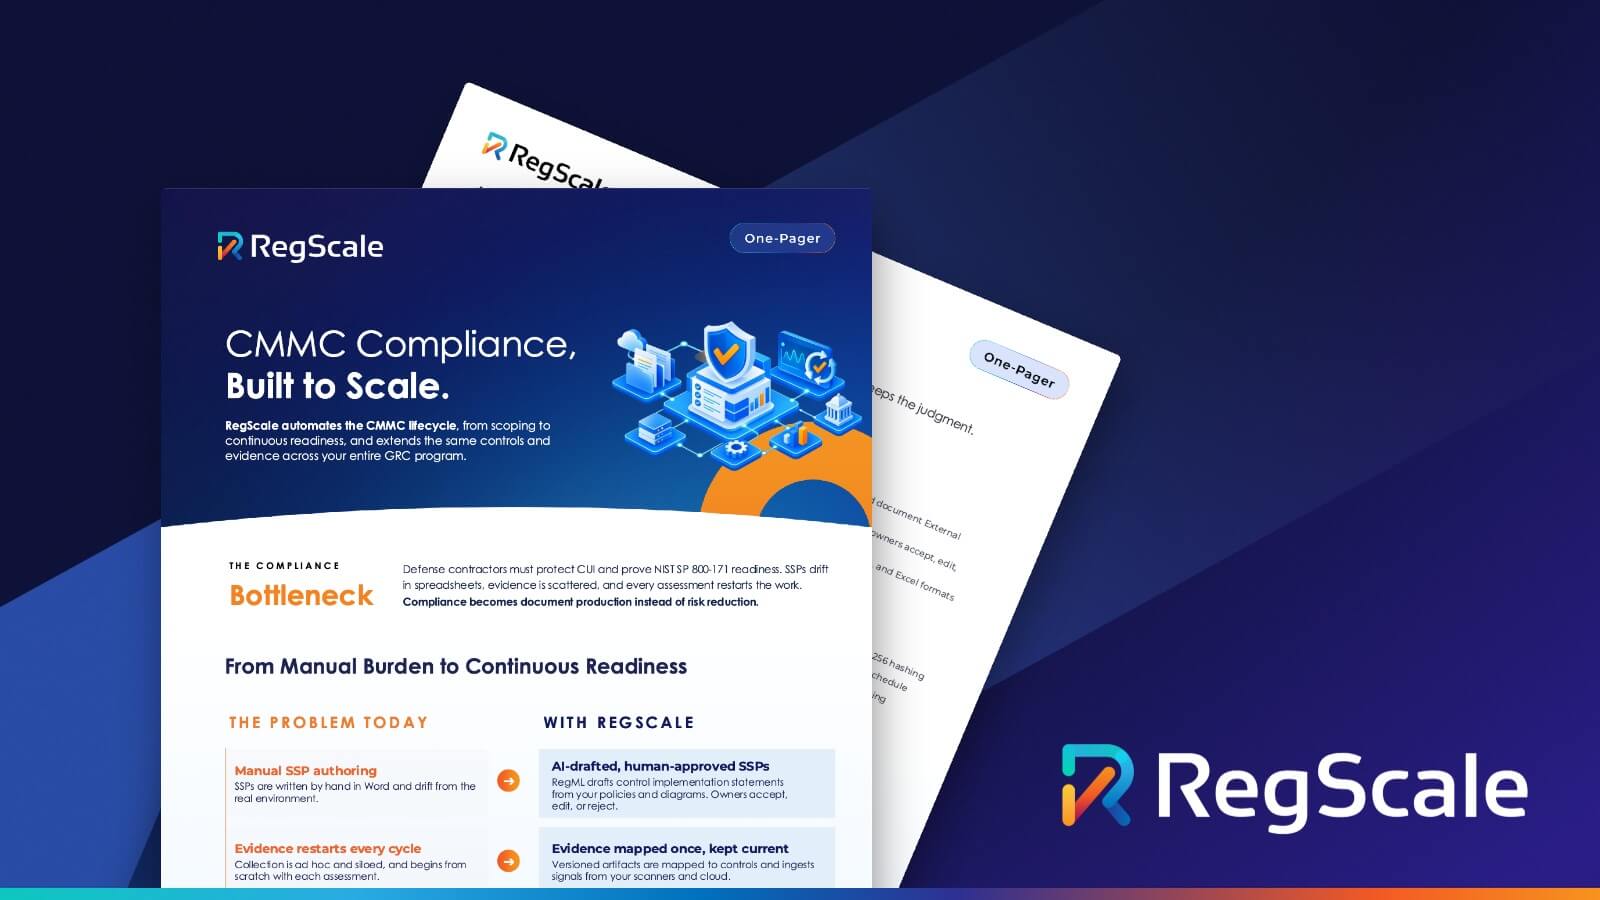
CMMC requires defense contractors to protect CUI and prove readiness against NIST SP 800-171. RegScale automates the full lifecycle, from scoping to continuous monitoring, and its open-standards architecture extends the same controls and evidence to your entire GRC program.
Download our one-pager to see how RegScale supports CMMC compliance through delivering:
- AI-drafted SSPs, reviewed and approved by your team
- Evidence mapped to controls once, with scheduled integrations
- AI Auditor gap checks against NIST SP 800-171 requirements
- SSP, SAP, SAR, and POA&M exports in OSCAL and Excel
- Cross-mapping to NIST 800-53, FedRAMP, ISO 27001, and SOC 2
Ready to make CMMC readiness continuous? See how RegScale can help.