RegScale’s Approach to FedRAMP VDR and VER
On December 7, 2026, FedRAMP retires severity-driven vulnerability management. Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) replace it, and every cloud service offering is measured against the new rules from that date. The change is not cosmetic. A Common Vulnerability Scoring System (CVSS) base score no longer sets a deadline on its own, evaluations have to be reproducible in front of an assessor, and agency customers expect to read your posture continuously instead of waiting on a monthly spreadsheet. RegScale evaluates findings against the CR26 risk rules and hands the result to Trust Center over an authenticated, read-only pipeline, so your agency customers and their Authorizing Officials see live posture without anyone on your security team compiling a package.
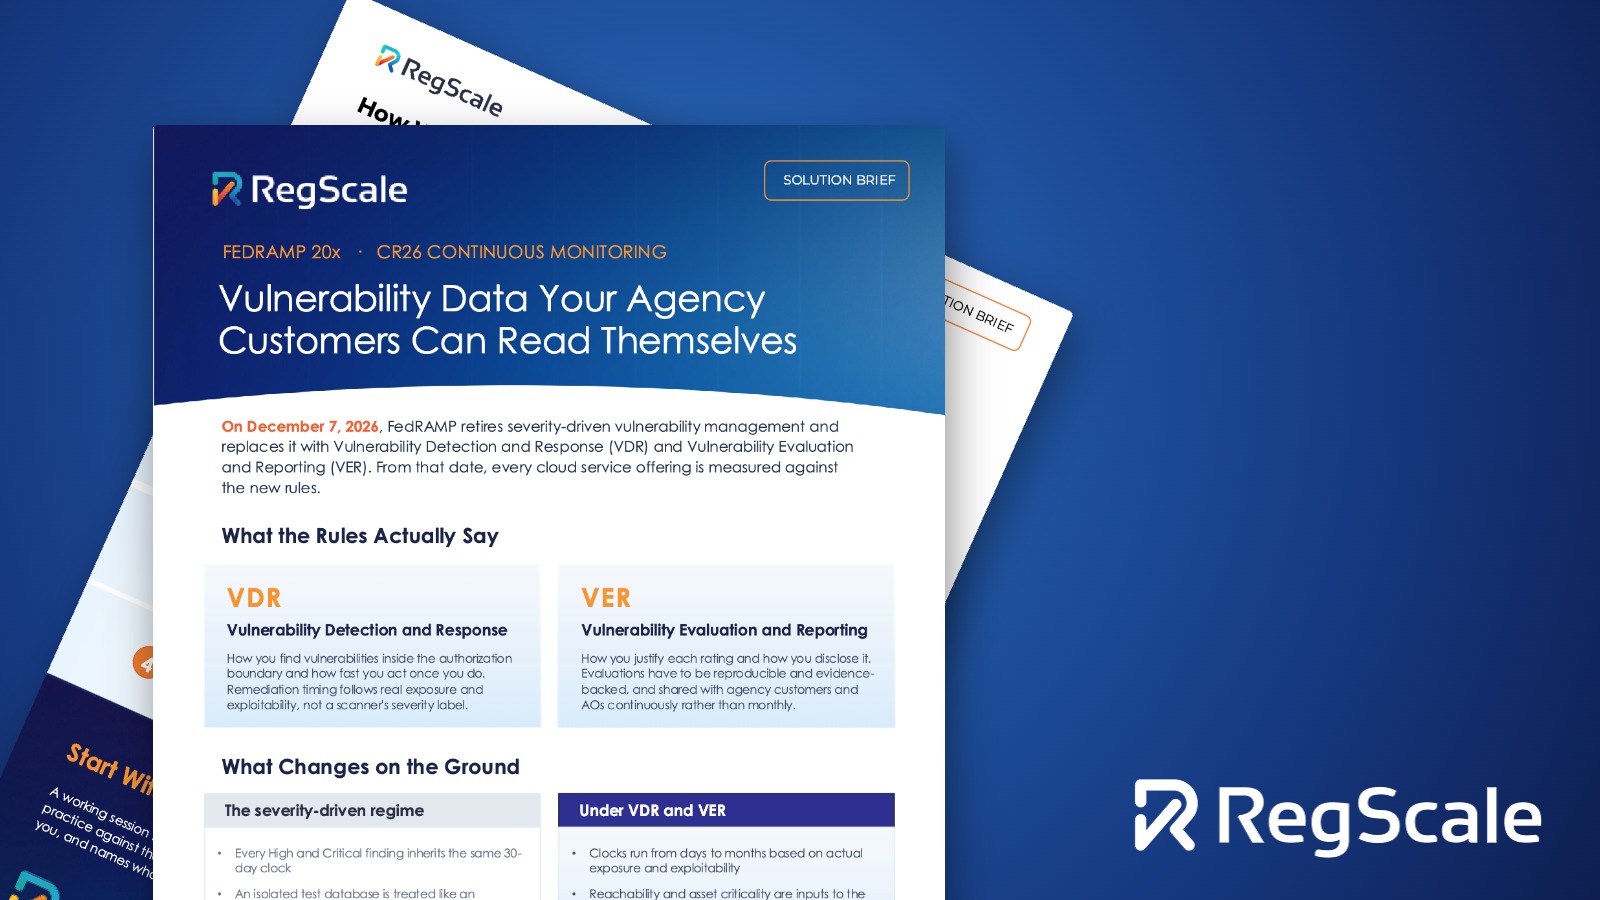
Download our one-pager to see how RegScale delivers VDR and VER:
- Risk-based evaluation that weighs public exposure, known exploitation, automatability, and degree of control instead of a scanner severity label
- A scoped OAuth 2.0 service account that gives Trust Center read-only access to the security plans you authorize, and nothing else
- Continuous ingestion of machine-readable Vulnerability Data Template (VDT), Assessment Validation Infrastructure (AVI), and High-Level Obligations (HLO) reporting on a scheduled sync, with no manual export step
- Live agency dashboards with Potential Adverse Impact (PAI) ratings, overdue metrics, and classifier exposure, scoped by multi-tenancy so each customer sees only the offerings they subscribe to
- Self-service continuous monitoring for AOs and ISSOs, covering compliance posture, risk acceptances, and mitigation reduction ladders on demand
Ready to have VDR and VER handled before the deadline instead of after it? See how RegScale can help.