Operate One Control Set Across Every Regulator
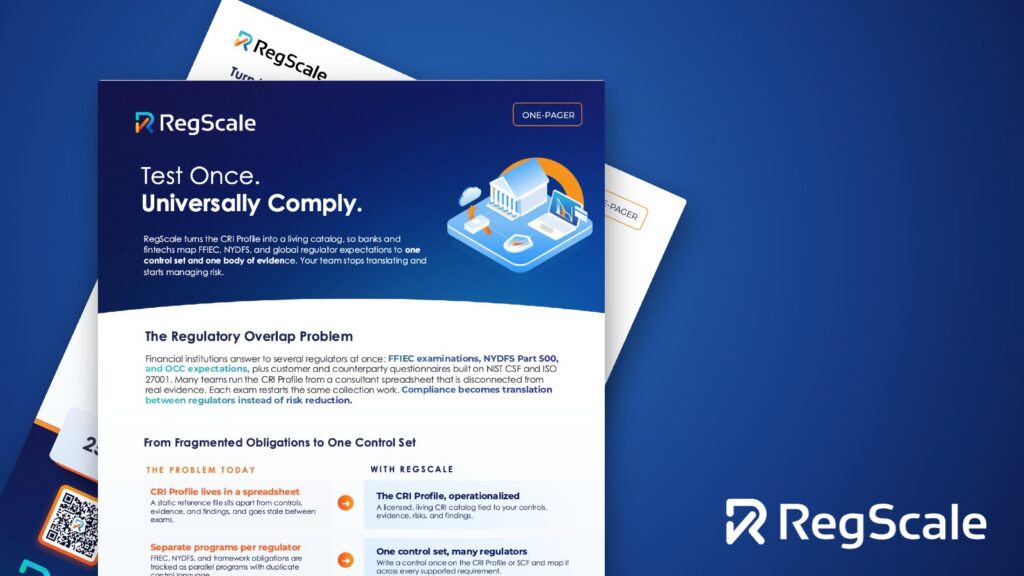
The FFIEC retired its Cybersecurity Assessment Tool on August 31, 2025, and the CRI Profile is now a common reference for banks and fintechs answering regulators. Many teams still run profiles and crosswalks from spreadsheets that are disconnected from real evidence, so each exam restarts the same collection work. RegScale operationalizes the CRI Profile, the SCF, and their mappings as living catalogs tied to your controls and evidence, so one control implementation satisfies every requirement mapped to it.
Download our one-pager to see how RegScale supports CRI Profile compliance for financial institutions through delivering
- A licensed, living CRI Profile catalog connected to your controls, evidence, risks, and findings
- Mapping to 250+ frameworks through the CRI Profile and SCF, including NYDFS Part 500, SOX, and PCI DSS
- Live evidence feeds from tools such as Wiz, Tenable, AWS, and Azure, mapped once to every requirement they satisfy
- Posture dashboards for the CISO and audit committee across every active regulator and framework
- RegML AI Author and AI Auditor to draft control language and review Security Plans before an exam
Ready to answer every regulator from one control set? See how RegScale can help.